Artificial intelligence is transforming financial services, helping banks automate operations, analyse customer behaviour, detect fraud, and improve decision making. However, as financial institutions become increasingly dependent on intelligent technologies, concerns about cybersecurity, data protection, and operational reliability are also growing.
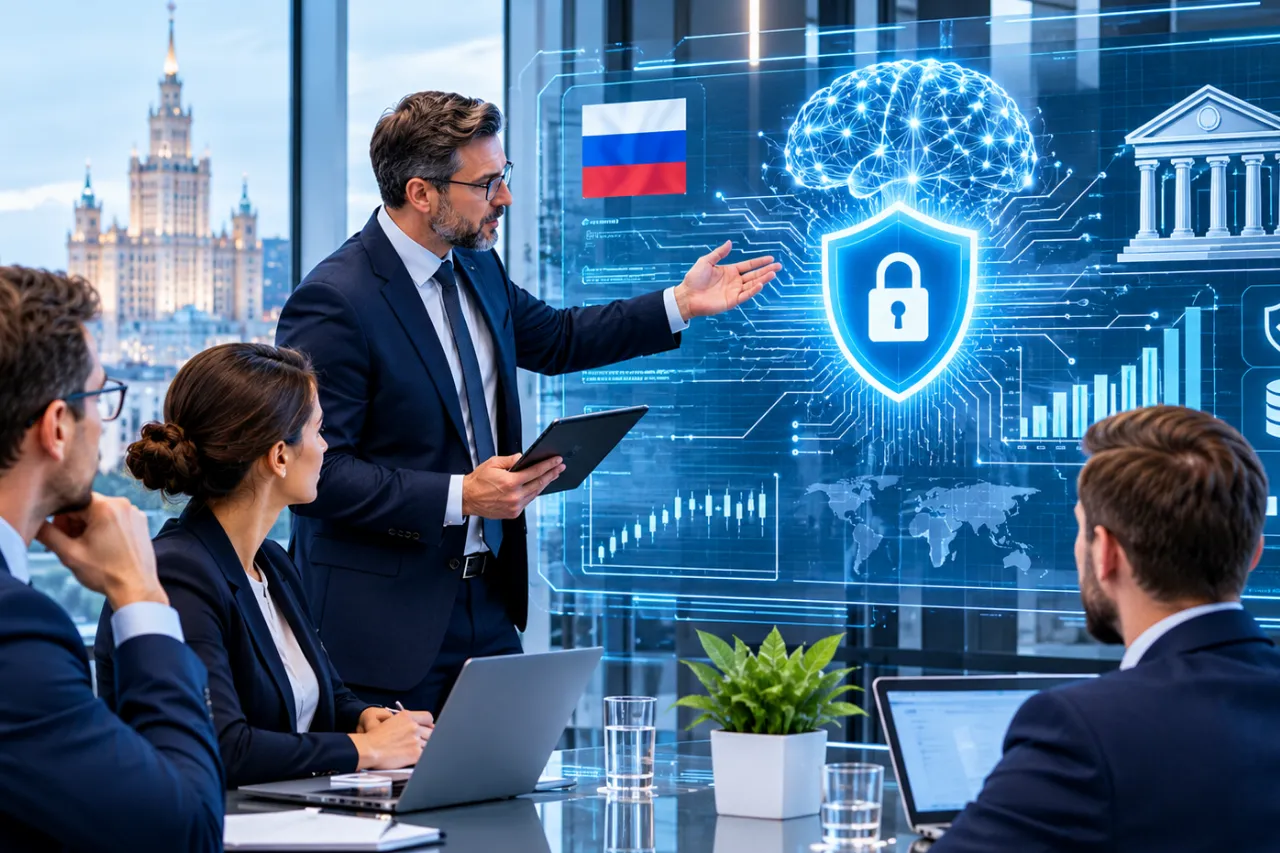
Recognising these challenges, the Bank of Russia published new methodological recommendations on 16 June 2026 to improve information security when financial organisations develop and use artificial intelligence. The document represents an important step towards strengthening responsible AI adoption across the Russian financial sector.
The AI safety guidelines aim to help financial institutions understand emerging technology related threats and introduce appropriate security measures. Moreover, they highlight the importance of maintaining human oversight when AI systems operate within critical financial processes.
Understanding the Main Risks of AI in Financial Services
AI systems can process enormous volumes of financial information, but their growing capabilities also create new vulnerabilities. Incorrect training data, compromised models, privacy violations, and unreliable outputs can affect the accuracy and security of financial operations.
For example, malicious actors may attempt to manipulate training datasets or exploit weaknesses in AI applications to influence their outputs. Similarly, confidential customer information could become exposed if organisations fail to implement appropriate data protection controls.
The Bank of Russia’s recommendations encourage financial institutions to identify these vulnerabilities before deploying AI technologies. Consequently, organisations are expected to consider information security throughout the development, testing, and operational stages of AI systems.
These developments reflect broader AI trends and insights, where cybersecurity is becoming an essential part of technological innovation rather than an afterthought.
Human Oversight Remains Essential in Critical Operations
One of the most important aspects of the recommendations concerns human involvement in high risk financial activities.
When AI systems perform automated operations within critical business processes, such as payment transactions, financial institutions are advised to introduce human validation if information security risks are assessed as high.
This means an employee should be able to review and modify the results generated by an AI system before an important operation is completed.
Such an approach can reduce the possibility of incorrect automated decisions affecting customers or disrupting financial services. Furthermore, it reinforces the principle that artificial intelligence should support financial professionals rather than replace accountability.
As machine learning advancements make automated systems increasingly sophisticated, maintaining appropriate human control will remain important for financial stability.
Financial Institutions Must Strengthen AI Governance
The Bank of Russia also recommends that financial organisations develop specific threat models and information security policies for AI technologies.
These internal frameworks should identify potential security weaknesses, define responsibilities, and establish suitable protection measures. Responsibility for preparing these documents is recommended to rest with the deputy head responsible for information security.
Additionally, institutions should regularly evaluate the performance and reliability of their AI systems.
This includes monitoring the quality of training data, protecting information during processing, and identifying unusual model behaviour. Therefore, AI governance must become an ongoing organisational responsibility involving technology specialists, risk managers, and senior leadership.
Third Party AI Providers Face Greater Security Expectations
Financial institutions frequently depend on external technology providers for AI models, cloud infrastructure, and specialised software components. Although these partnerships can accelerate innovation, they may also introduce additional cybersecurity risks.
The Bank of Russia’s recommendations address information security when organisations use AI services supplied by external vendors.
Financial institutions are encouraged to assess the security practices of technology providers, monitor potential vulnerabilities, and understand how external AI systems handle sensitive information.
For example, participation in vulnerability discovery programmes, such as bug bounty initiatives, can provide additional confidence in a provider’s security practices.
Furthermore, organisations should pay attention to the integrity of externally supplied models and datasets throughout the technology supply chain.
These measures are particularly relevant as generative AI developments and open source technologies become more widely integrated into financial operations.
AI Automation Creates New Opportunities and Challenges
Despite security concerns, artificial intelligence continues to offer significant opportunities for financial institutions.
Automated systems can support fraud detection, customer service, regulatory monitoring, financial analysis, and operational reporting. Moreover, predictive technologies can help organisations recognise unusual patterns and respond to potential threats more efficiently.
However, successful implementation requires a balance between innovation and risk management.
Financial institutions must evaluate whether an AI application is appropriate for a particular business process before introducing it. They should also establish clear procedures for monitoring system performance and responding to security incidents.
These priorities demonstrate how automation and future tech can improve financial services when supported by appropriate safeguards.
What the Guidelines Mean for the Future of AI in Finance
The Bank of Russia’s recommendations reflect a broader shift towards responsible artificial intelligence adoption in financial services.
Regulators and financial institutions are increasingly recognising that AI security involves more than protecting software. It also requires reliable data management, transparent decision making, employee awareness, and effective oversight.
Furthermore, international discussions around AI governance are reinforcing the need for organisations to manage risks throughout the entire technology lifecycle.
As AI industry updates continue to highlight new applications and emerging threats, financial institutions will need to regularly review their security frameworks and adapt to future technological developments.
Future of AI research will also play an important role in understanding how advanced models can be made more secure, reliable, and accountable.
Actionable Insights for Financial Organisations
Financial institutions should treat AI security as a core part of their digital transformation strategy. Before deploying new technologies, organisations should assess potential vulnerabilities, establish clear security policies, and determine which decisions require human approval.
Additionally, regular testing of AI models, employee training, third party assessments, and continuous monitoring can help reduce operational risks.
Most importantly, organisations should avoid relying entirely on automated outputs when critical financial decisions are involved. A combination of intelligent technology and qualified human oversight can support safer and more reliable financial services.
Stay informed about emerging AI technologies, cybersecurity developments, and responsible innovation with AITechInfoPro. Connect with our team to explore valuable technology insights and discover how artificial intelligence is shaping the future of business.
Source – akm